Home / Technology / Hackers Trick Users Into Installing Malware Via Reddit Ads
Hackers Trick Users Into Installing Malware Via Reddit Ads
14 Sep
Summary
- New 'ClickFix' attacks exploit users via fake ads on Reddit.
- Malware is installed by tricking users into pasting commands.
- Info-stealing malware targets passwords and crypto wallets.
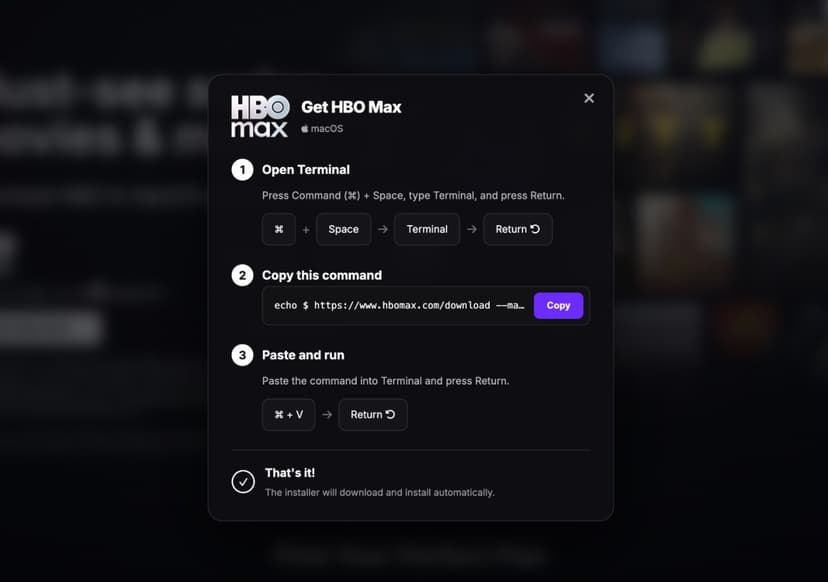
A new wave of cyber threats, known as 'ClickFix' attacks, has emerged, leveraging fake advertisements on platforms like Reddit to compromise user devices. Recent campaigns have involved hackers posting deceptive ads that mimic HBO Max, leading unsuspecting users to malicious websites or compromised legitimate sites. These sites present a fake CAPTCHA or anti-bot check, which, when clicked, instructs users to execute commands in their system's terminal.
Upon executing these commands, users inadvertently install info-stealing malware. This malware is designed to immediately steal sensitive information, including passwords, access to logged-in accounts, and cryptocurrency wallets. The method of execution within the system's terminal allows these attacks to often bypass standard antivirus and security defenses, making them particularly insidious.
The latest observed ClickFix campaign utilized compromised HBO Max accounts on Reddit to spread numerous fake advertisements. Security researchers have documented this sophisticated international effort, though the exact number of affected users remains undetermined. Companies are advised to implement domain-wide blocks on terminal access for Windows machines, and specific tools like BlockBlock offer defenses for Mac users.


